TLDR
- On September 17, 2026, Texas Attorney General Ken Paxton issued a consumer alert about demand letters sent to Texas businesses and nonprofits.
- The letters claim that everyday website tools (cookies, pixels, analytics, search bars, and similar scripts) violate California’s Invasion of Privacy Act (CIPA) and often demand payment to avoid a lawsuit.
- The AG urged organizations to be careful, consult counsel before paying or replying, and report suspected fraud.
- This is not a new Texas opt-in cookie rule. It is a warning about how some CIPA-based demands are framed.
- For Shopify and ecommerce teams everywhere, the practical lesson is simple: know what your site collects and shares with third parties before a demand letter puts those tools under a microscope.
What the Texas AG said on September 17, 2026
Attorney General Ken Paxton’s office warned Texas businesses and nonprofit organizations about a surge in demand letters that allege website privacy violations under California law, specifically the California Invasion of Privacy Act (CIPA).
According to the official consumer alert, those letters often point to common website technologies, including:
- cookies
- tracking pixels
- analytics tools
- search bars
- and similar third-party scripts
Senders may argue that these tools amount to unlawful “wiretapping” under California law. Packages can look formal and intimidating. They may include screenshots of your website, a draft complaint, and a demand for payment to avoid litigation.
Paxton’s office advised recipients to exercise caution and seek legal guidance before taking action. The alert states that demand letters of this type may exaggerate or misrepresent a potential violation of law. Organizations should not respond directly to the sender or pay without first consulting qualified legal counsel when possible.
The AG also pointed to one serial CIPA plaintiff associated with these demand letters who has been declared a vexatious litigant and is restricted from filing new CIPA or related digital privacy claims in the U.S. District Court for the Central District of California without court permission. That context can matter when evaluating a letter, but it does not replace a case-by-case legal review.
Texas businesses and organizations that believe a CIPA demand is fraudulent, abusive, or deceptive can report it to the Texas Attorney General’s Consumer Protection Division (toll-free 1-800-621-0508 or via the online complaint form).
What this alert is not
A few clarifications matter for merchants who only skim the headline.
Texas did not create a new opt-in cookie requirement with this alert.
The warning is about demand letters that rely on California’s CIPA, not a new Texas statute that forces every Texas store to run GDPR-style prior consent for all cookies.
A demand letter is not a finding that you violated CIPA.
It is one side’s allegation. Receiving mail or email that looks like a lawsuit package does not mean a court has decided anything about your store.
Using cookies, analytics, pixels, or other common website technologies does not automatically create liability.
Whether CIPA (or any similar claim) applies depends on the facts: how the site is set up, what data is involved, which visitors are involved, which technologies run, what they transmit, and other legal factors. Fisher Phillips makes the same point in its analysis: routine use of analytics or ads tools is not, by itself, proof of liability, and the right response still turns on the specific allegations and configuration.
Do not treat this as a blanket rule that “all Texas businesses must switch to opt-in consent.”
Consent design should follow your real visitor mix, the laws that actually apply to you, and advice from qualified counsel. The AG’s message is closer to: slow down, verify the claim, and understand your own stack before you write a check.
Why ecommerce teams outside California still care
Many Shopify stores ship nationwide. California visitors still land on product pages, use site search, open chat widgets, and click ads that fire pixels. Demand letters that cite California law can reach businesses headquartered in Texas, or anywhere else, if the sender ties the claim to California visitors or California privacy theories.
You do not need a California warehouse to get a letter that claims CIPA exposure. That is why the AG’s warning lands for ecommerce operators in general, not only Texas nonprofits and brick-and-mortar shops.
The useful takeaway is not panic. It is visibility.
Do you know which trackers are running on your site, what data they collect, when they start collecting it, and which third parties receive it?
If the honest answer is “not really,” that is the gap to close. Don’t wait for a demand letter to find out what your website is sending to third parties. The Texas AG’s warning is a reminder that businesses should understand their website tracking before a complaint puts it under scrutiny.
What should businesses check now?
Use this as a practical storefront audit, not a substitute for legal advice.
1. Inventory every third-party technology on the storefront
List cookies, pixels, analytics platforms, advertising scripts, chat tools, session-replay products, site-search widgets, tag managers, and other scripts that load on product, collection, cart, and checkout-related pages. Include apps you installed months ago and forgot about.
2. See what loads before any visitor choice
Open the store in a fresh private window. Note what fires before someone interacts with a cookie banner or preference center. Timing often matters in how claims are framed, even when the legal outcome is fact-specific.
3. Map what each tool receives
For each vendor, document identifiers, page URLs, product views, search queries, form fields, event names, and any other signals that show what a visitor did on the site. Site search terms and high-intent paths (wishlist, cart, account) deserve extra attention because they can reveal more than a simple page view.
4. Review banners, consent settings, and privacy disclosures
Check that your public privacy notice and cookie disclosures match the tools that actually run. Confirm region rules, default states, and what “accept,” “reject,” and preference controls do in practice. Keep records of consent where your setup and applicable rules call for them.
5. Rescan after app and theme changes
New Shopify apps, pixels, and theme edits can introduce trackers without a marketing kickoff meeting. Schedule regular scans so the inventory stays current.
6. Keep basic documentation
Save configurations, consent settings, privacy notice versions, scan results, and vendor lists. If a letter arrives, that paper trail helps counsel respond with facts instead of guesses.
7. If a demand letter arrives
- Preserve the full package: letter, attachments, screenshots, draft complaint, emails, headers, payment instructions, envelope or postmark.
- Preserve relevant site versions, consent logs, vendor agreements, and tag settings tied to the allegations.
- Do not pay, admit fault, or send a detailed technical reply before qualified privacy counsel reviews the claim.
- Texas organizations that suspect fraud or abuse can report it through the AG channels above. Counsel can advise whether other reports make sense in your situation.
The AG’s own checklist is short and aligned with this: consult privacy-experienced counsel, review pixels/cookies/analytics with that counsel, and keep watching how courts and laws treat website-tracking tools. (Texas AG consumer alert)
How Consentmo can support the “know your stack” work
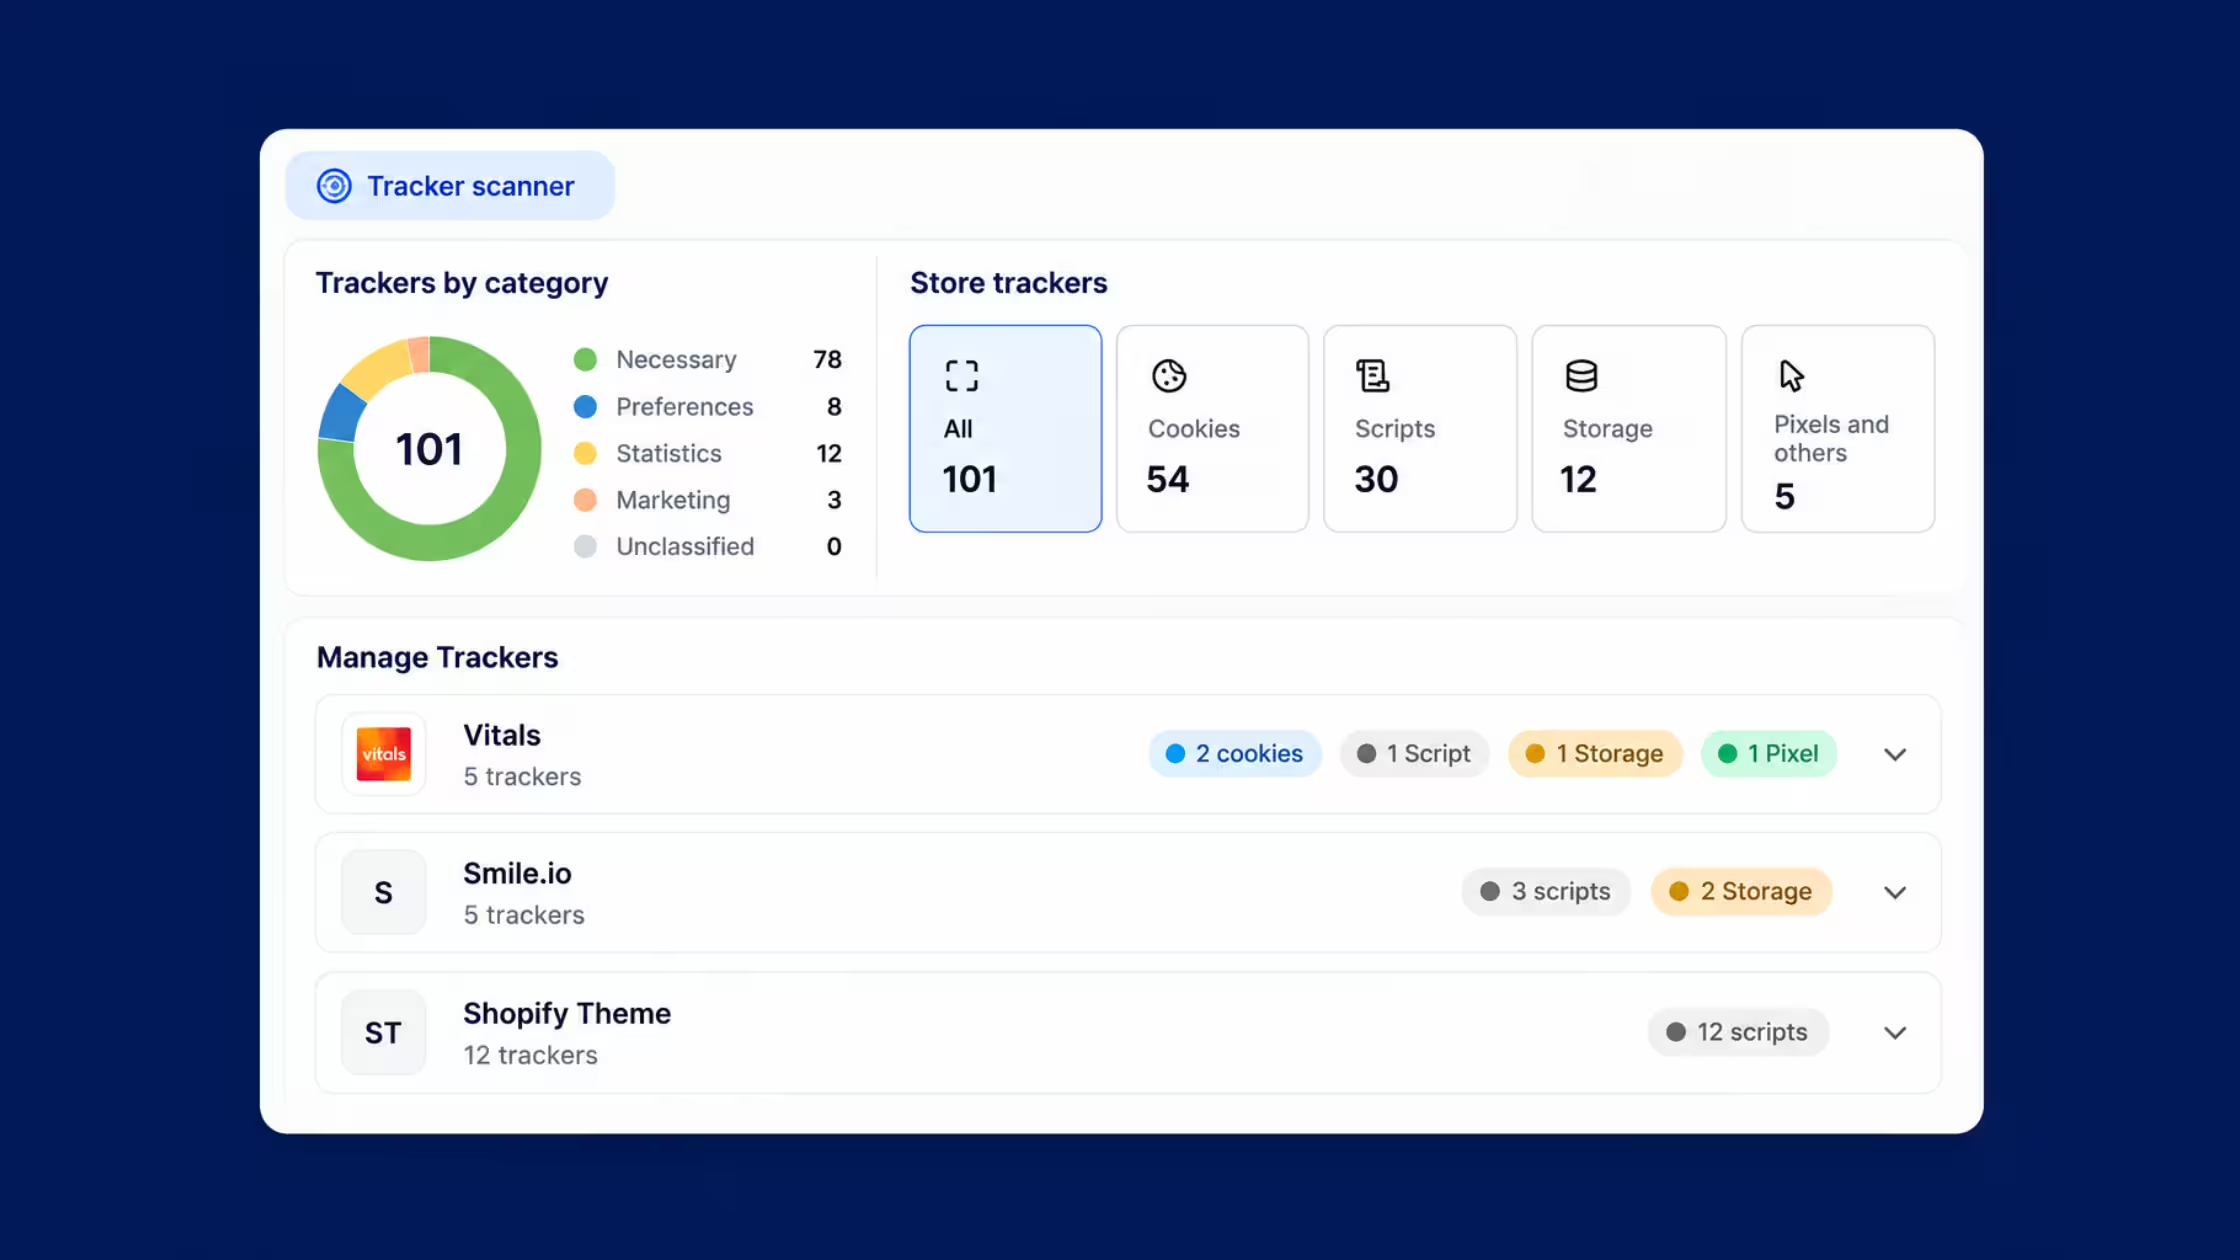
Visibility and consent controls will not erase every CIPA theory, and a cookie consent manager does not guarantee protection from CIPA claims or replace legal advice. For Shopify merchants who want a clearer picture of what runs on the store, Consentmo can help you:
- scan the store for cookies and trackers
- identify and categorize third-party technologies
- review which trackers are active
- manage cookie consent and visitor preferences
- configure consent behavior based on visitor location
- block applicable analytics and marketing technologies until consent, where you configure that behavior
- maintain consent records
- detect changes and new integrations over time
Pair that operational visibility with counsel when a letter shows up, and with honest privacy copy that matches real data flows. That combination is far more useful than rushing a payment because a PDF looked official.
For related Consentmo reading on California tracking risk and cautious consent design, see California Tracking Lawsuits Are Rising.
Bottom line
The September 17, 2026 Texas AG alert is a consumer-protection warning about how some CIPA demand letters are used, not a new Texas cookie opt-in mandate. Letters may name ordinary website tools, attach screenshots, and push for quick payment. Some claims may overstate exposure. Recipients should slow down and get legal advice.
For ecommerce teams, the calm, useful response is prevention through clarity:
- Know your trackers.
- Know what they collect and when.
- Know who receives the data.
- Keep disclosures and consent settings aligned with reality.
- If a demand arrives, preserve everything and call counsel before you pay or reply.
Don’t wait for a demand letter to find out what your website is sending to third parties.
This article is for general information for ecommerce and marketing teams. It is not legal advice. CIPA and related claims turn on specific facts. Consult qualified counsel about your situation.