How to Make Your Shopify Store Compliant with CCPA/CPRA "Do Not Sell or Share" Rules
If your business targets or serves consumers in California, ensuring your Shopify store adheres to the California Consumer Privacy Act (CCPA) and California Privacy Rights Act (CPRA) is essential for avoiding regulatory scrutiny and legal claims. One of the core mandates under CCPA/CPRA is providing a clear, accessible way for consumers to exercise their right to opt out of the sale or sharing of their personal information.
In this guide, we break down what the "Do Not Sell or Share My Personal Information" rule requires, how CPRA expanded these mandates, and how to configure Consentmo on your Shopify store to stay fully compliant.
What is the CCPA/CPRA "Do Not Sell or Share" Rule?
California privacy law grants residents the right to direct businesses to stop selling or sharing their personal information with third parties. Under the expanded CPRA framework, "sharing" explicitly covers cross-context behavioral advertising, targeted marketing pixels, and third-party data collection scripts.
To fulfill CCPA/CPRA opt-out requirements, your Shopify store must meet five key criteria:
- Dedicated Opt-Out Section: A clear mechanism allowing visitors to submit a "Do Not Sell or Share My Personal Information" request.
- Homepage & Footer Link: An accessible link in your store's main footer menu taking visitors directly to the opt-out mechanism.
- No Account Required: Consumers must be able to submit opt-out requests without needing to create an account or register.
- Privacy Policy Disclosure: Your Privacy Policy must explicitly detail consumer opt-out rights and link directly to your opt-out page.
- Automated & Universal Preference Signals: Your store must recognize and honor browser-level opt-out preference signals, such as Global Privacy Control (GPC), treating them as valid, direct opt-out requests.
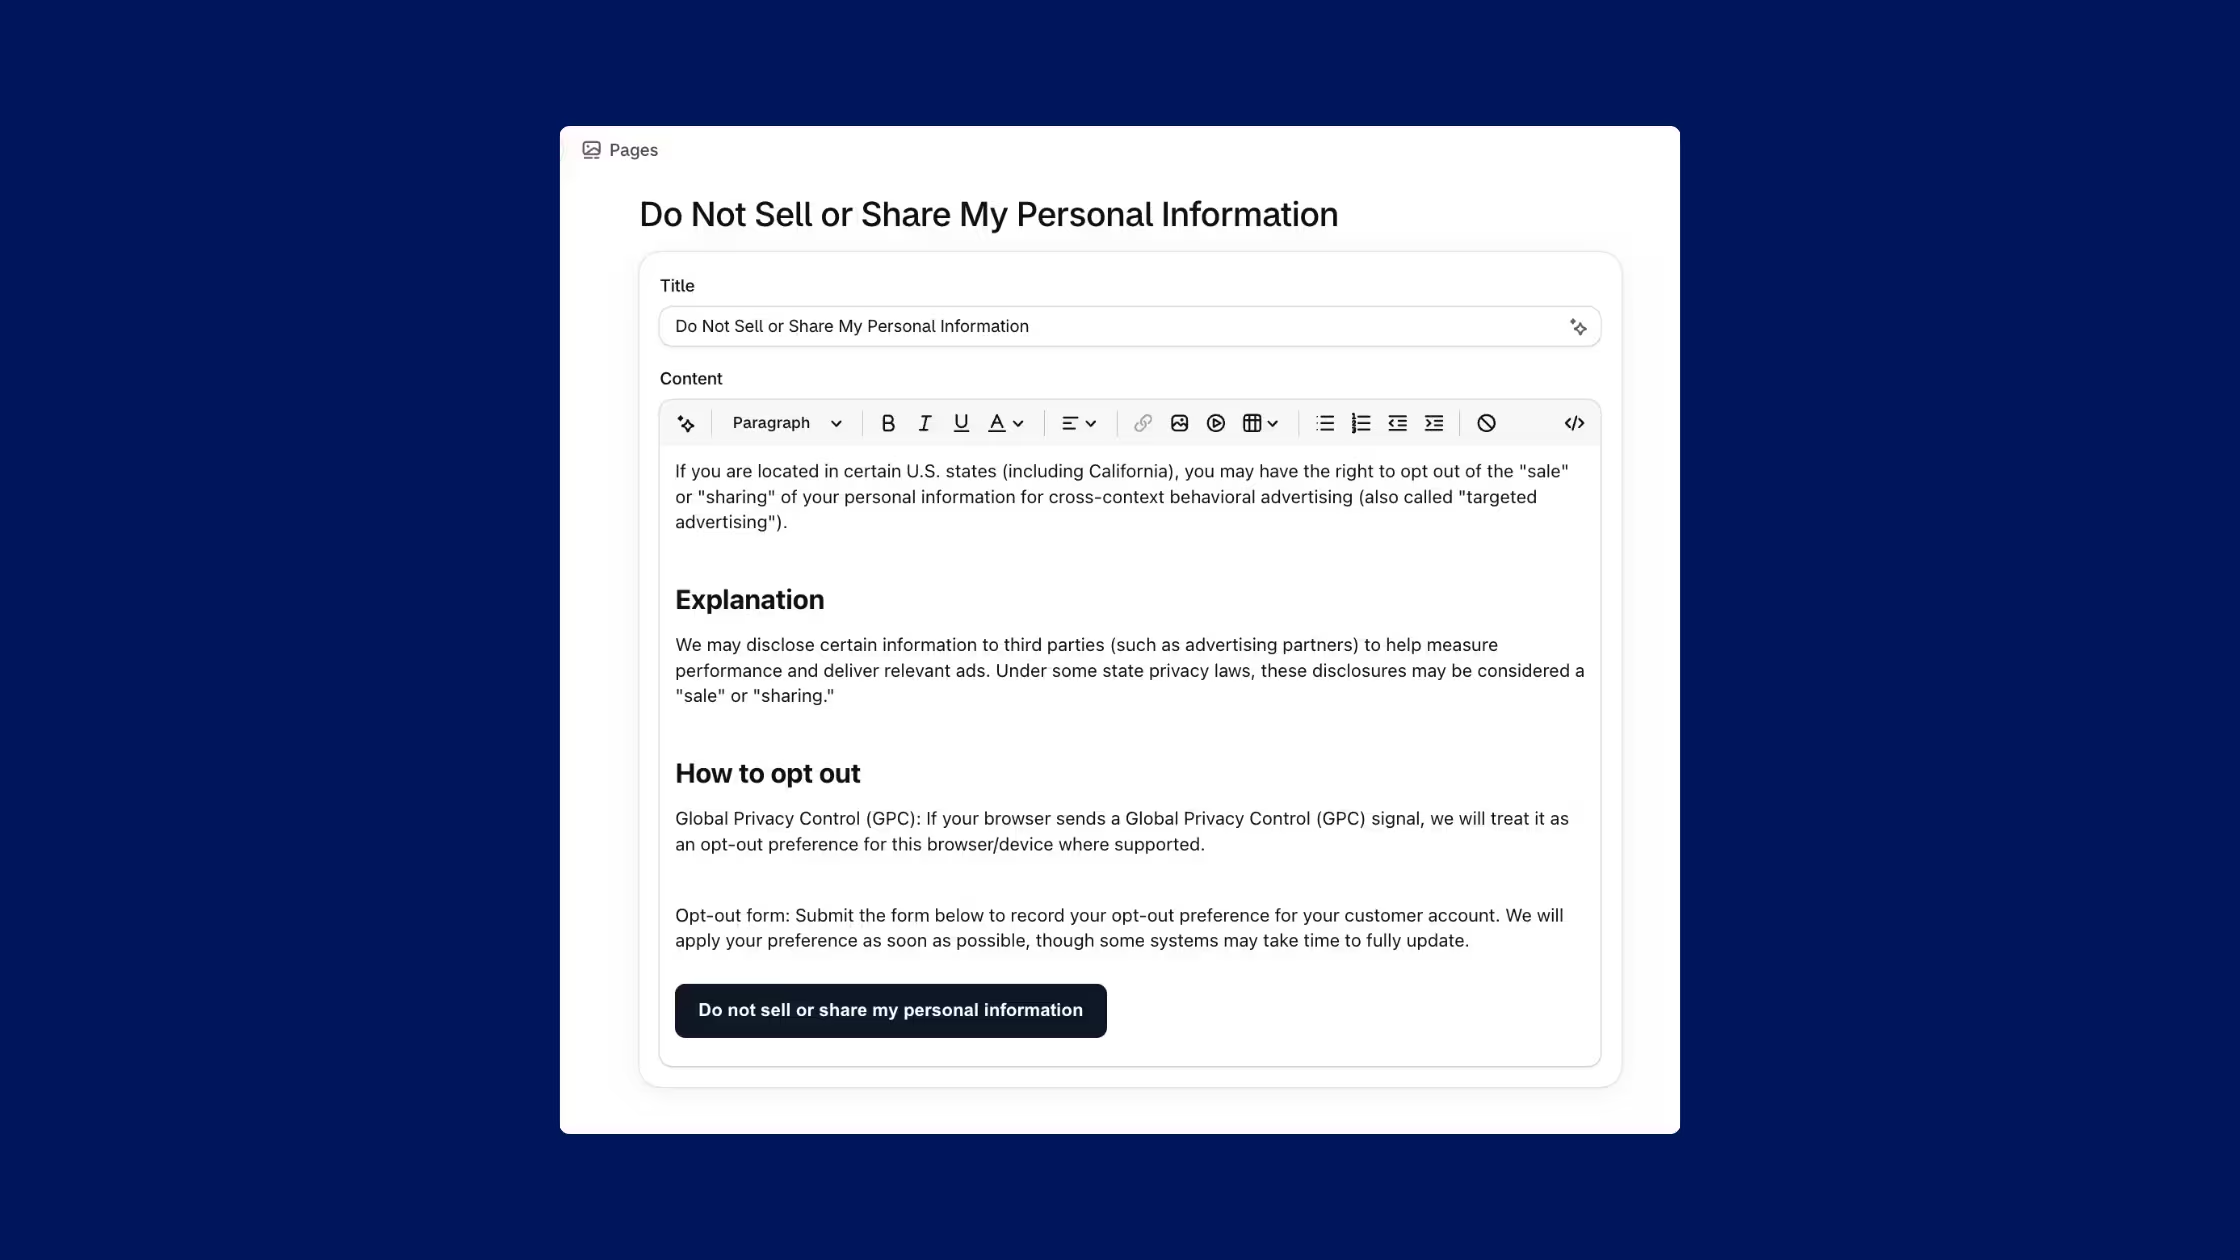
How to Set Up "Do Not Sell or Share" in Consentmo
Consentmo automates CCPA/CPRA compliance on Shopify by updating your compliance pages, managing customer preferences, and emitting privacy signals directly to compliant tracking scripts.
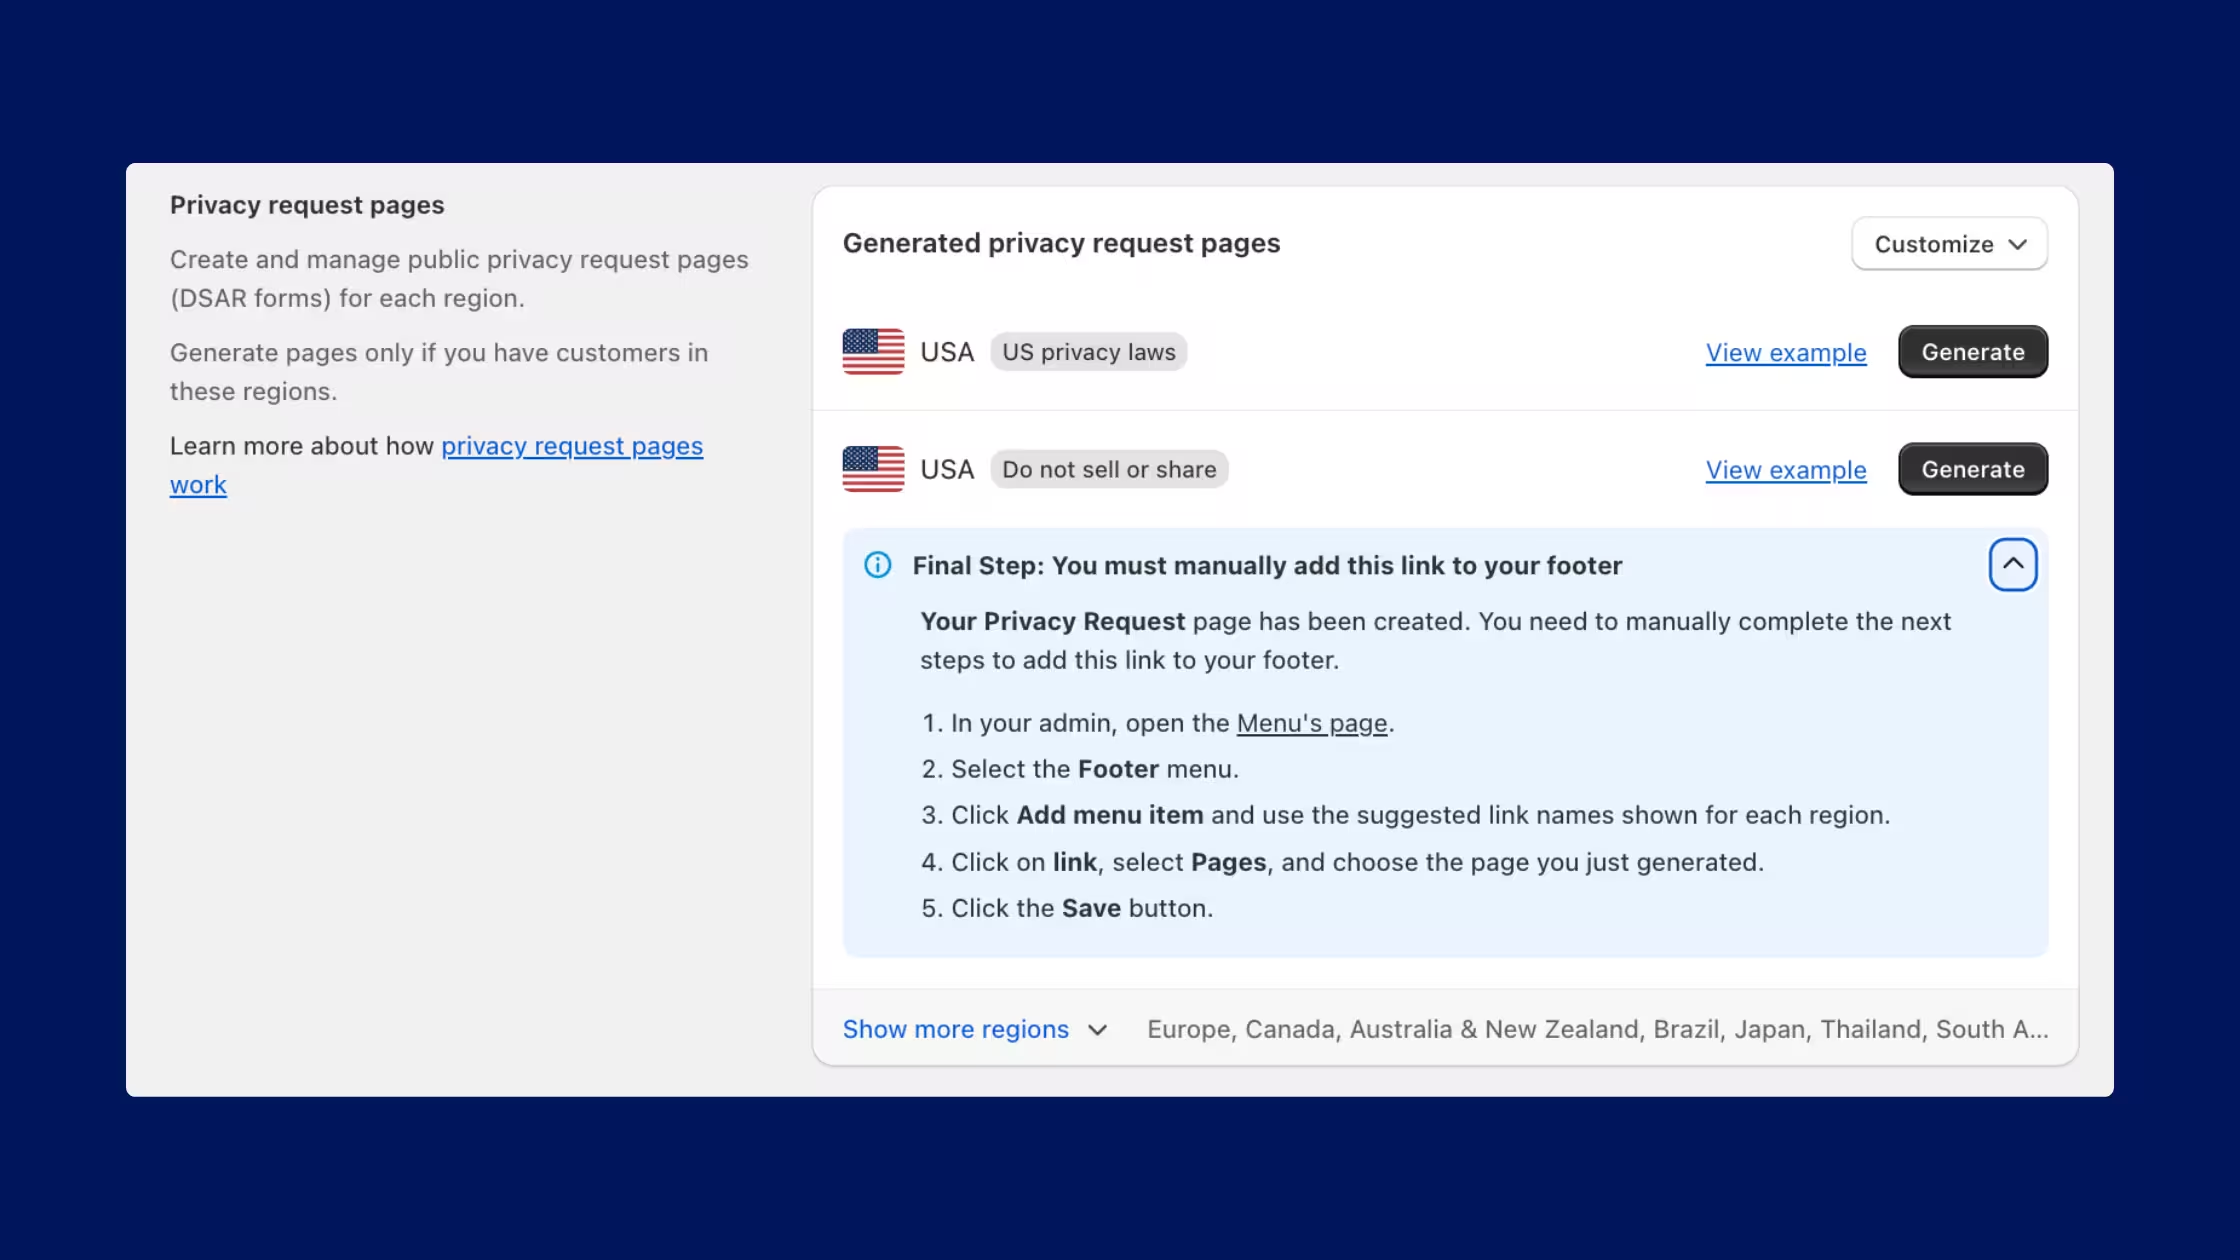
Step 1: Enable & Review Your CCPA/CPRA Compliance Page
- Open the Consentmo app in your Shopify admin.
- Navigate to Privacy center > Privacy request pages.
- Click on Generate.
Step 2: Add the Direct Opt-Out Link to Your Shopify Footer
California law requires a clear link in your storefront footer menu so consumers can trigger their opt-out right from any page on your store.
- In your admin, open the .
- Select the Footer menu.
- Click Add menu item and use the suggested link names shown for each region.
- Click on link, select Pages, and choose the page you just generated.
- Click the Save button.
Ensuring Full CPRA & GPC Compliance
Beyond static opt-out forms, CPRA requires businesses to process opt-outs dynamically across modern browser standards:
- Global Privacy Control (GPC): Consentmo automatically detects GPC signals sent by modern browsers and disables targeted tracking scripts without requiring manual form entry.
- Cookie & Script Blocking: When a user opts out, Consentmo updates the visitor's state to prevent Meta Pixel, Google Analytics, and third-party ad tags from processing personal data for targeted advertising.
- Logged Requests: All opt-out requests submitted via your compliance page are logged in your Consentmo dashboard, creating a verifiable audit trail for compliance monitoring.
By pairing Consentmo's automated compliance pages with a direct footer link and GPC detection, your Shopify store meets current California privacy standards seamlessly.
For questions or assistance with your setup, reach out to our team via in-app chat.